VPSLAB
Overview
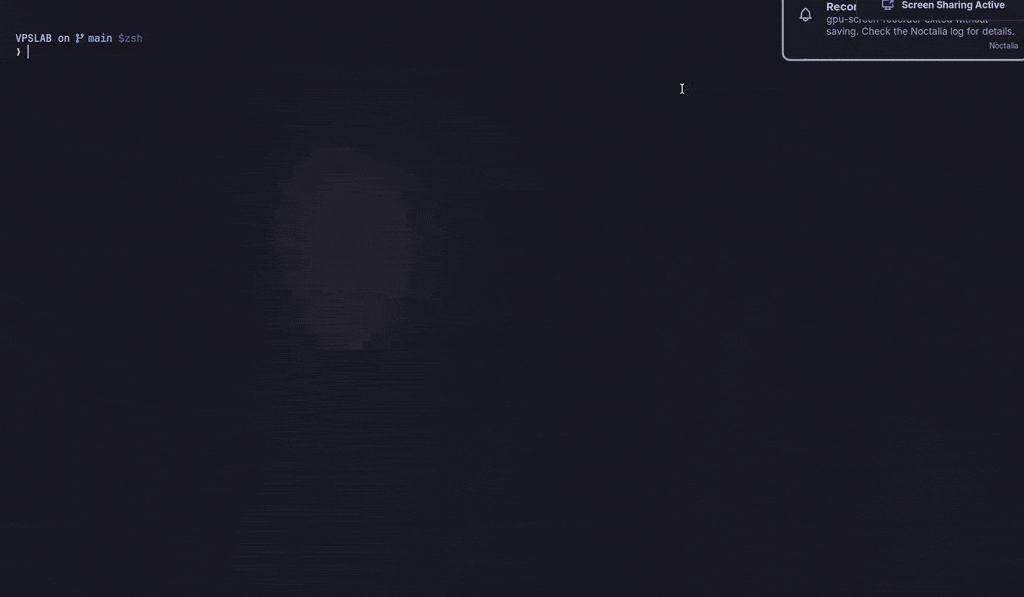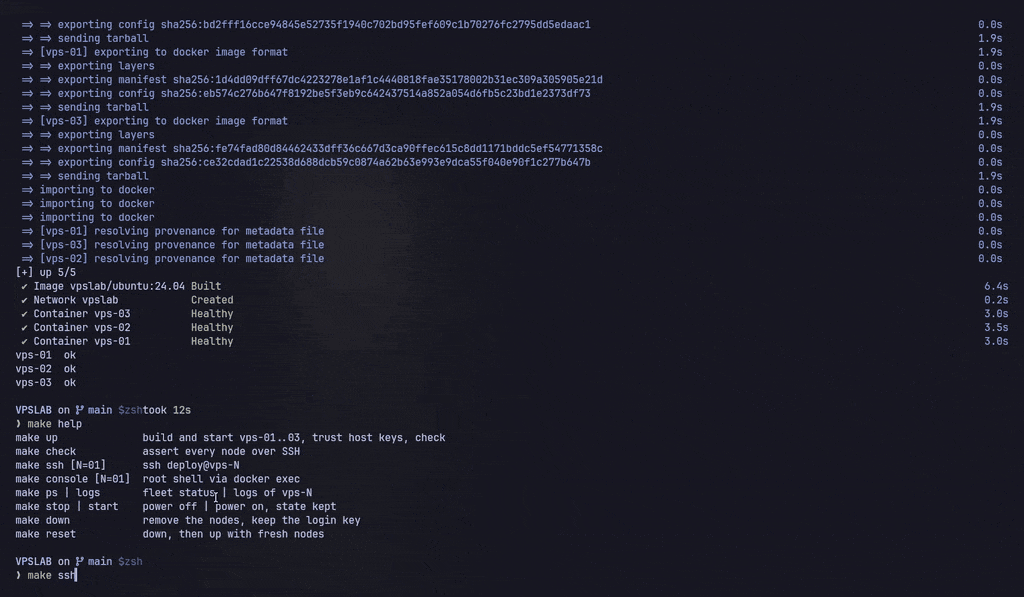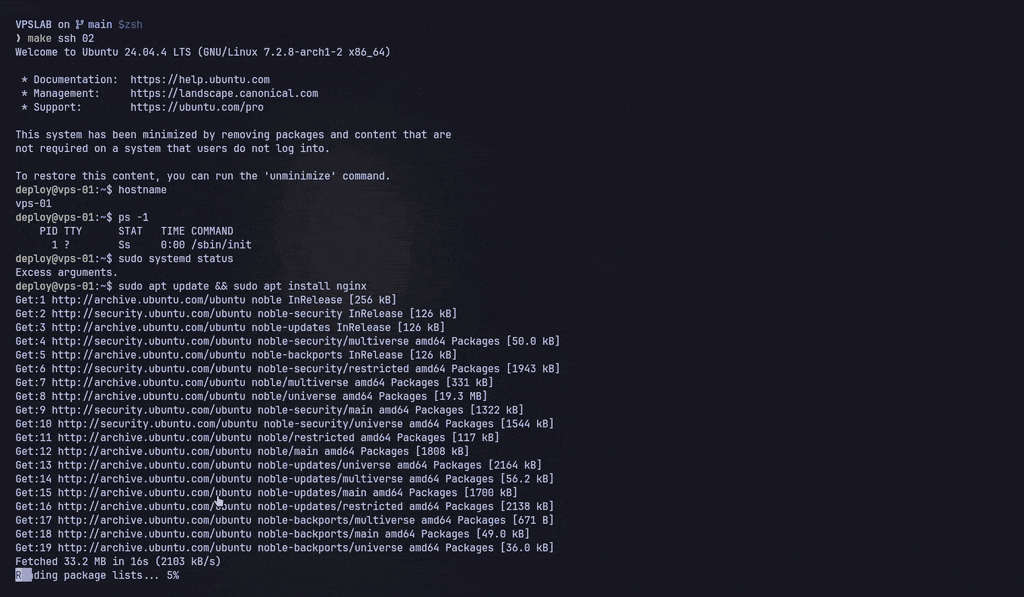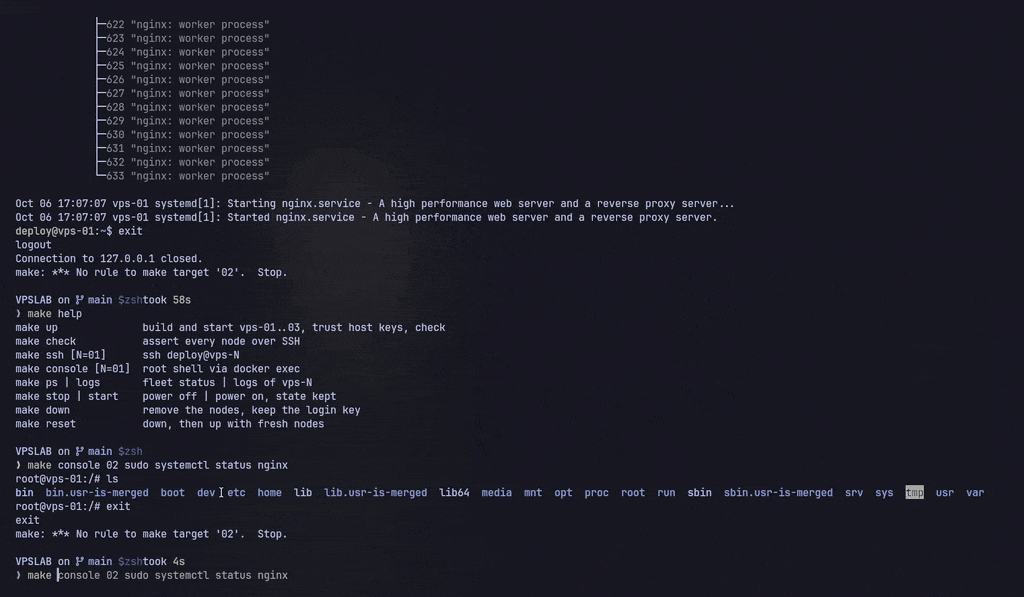
A one-command lab of three Ubuntu 24.04 nodes that look and act like small VPSes: systemd runs as PID 1 so real services, timers, and logs can be exercised, each node has a static private IP and a localhost SSH port, and packages install with apt. `make up` builds the image, starts the fleet, generates a login key, and pins every node's host key read straight from the container, so the first SSH connection is already verified. Nodes run without --privileged; the only added capabilities are NET_ADMIN and SYS_ADMIN, the latter because systemd otherwise silently skips unit sandboxing and a hardened unit that fails on a real server would pass here. A 38-check smoke suite asserts identity, SSH policy, networking, sandboxing, isolation, and resource caps, and every privilege decision is backed by recorded experiments.
Highlights
- Built a three-node fleet of disposable Ubuntu 24.04 servers with systemd as PID 1, sshd, cron, and journald, each with a static private IP and capped at 1 CPU, 1 GiB, and 2048 processes
- Made the first SSH connection verified by reading each node's host key directly from the container and generating known_hosts and an ssh_config on every make up
- Kept nodes unprivileged, adding only NET_ADMIN and SYS_ADMIN, and proved with recorded experiments that SYS_ADMIN is what lets systemd apply unit sandboxing (ProtectSystem, PrivateTmp)
- Wrote a 38-check smoke suite covering identity, SSH policy, networking, sandboxing, isolation, and resource caps, asserting that the host clock and block devices stay out of reach